
Cloud security posture management
Every account checked against the CIS Benchmarks, with fixes written in Terraform so they do not drift back.
Our cloud security and compliance services close the gaps in your AWS, Azure or Google Cloud setup and prove it to customers, auditors and regulators. Certified engineers fix misconfigurations, tighten access, encrypt data, switch on audit logs and map each control to SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR or India's DPDP Act.
 4.9
 Written by Abhishek Kumar, Content Writer



















Cloud security and compliance services protect the data, identities and workloads you run on AWS, Azure or Google Cloud, and prove those protections meet frameworks such as SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR and the DPDP Act.
Identity and logging come first; every later control depends on them.
Get a free proposalEvery account checked against the CIS Benchmarks, with fixes written in Terraform so they do not drift back.
MFA and single sign-on through IAM Identity Center or Microsoft Entra ID, with least-privilege roles.
Encryption at rest and in transit, and secrets moved out of code into a secrets manager.
Audit logs centralized and protected, with threat findings routed to our cloud infrastructure monitoring team.
Private subnets, a web application firewall, patching and image scanning; our Kubernetes team locks down clusters.
Controls mapped to your frameworks, plain-language policies and evidence collected as you go.
The changes that show up first.
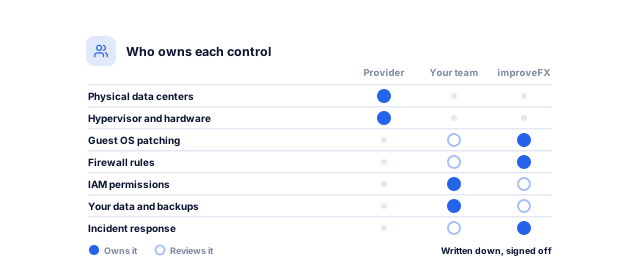
AWS describes its job as security of the cloud and yours as security in the cloud. We write down who owns each control across your team, your provider and us.
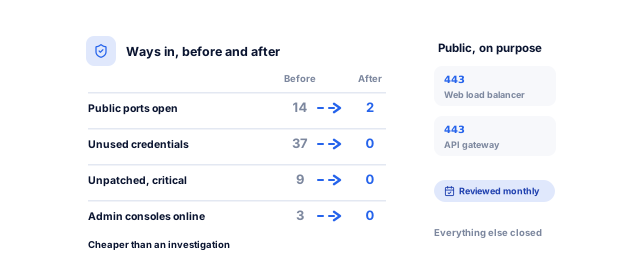
Software vulnerabilities were the starting point for 31% of breaches in the Verizon 2026 Data Breach Investigations Report. Patching, closed ports and deleted credentials cut the doors an attacker can try.
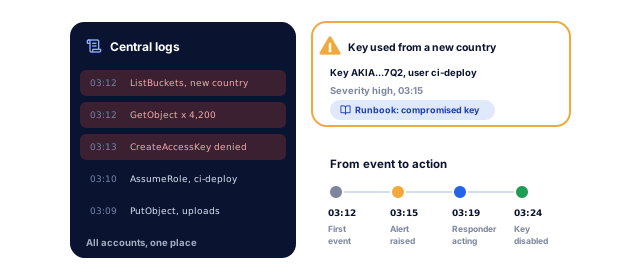
The global average cost of a data breach reached $4.99 million in the IBM Cost of a Data Breach Report 2026. Central logs, tuned alerts and a tested runbook mean faster action.
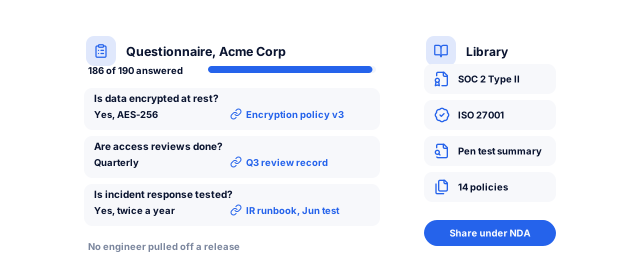
With controls and evidence ready, your team answers enterprise questionnaires from a prepared library instead of stalling the sale.
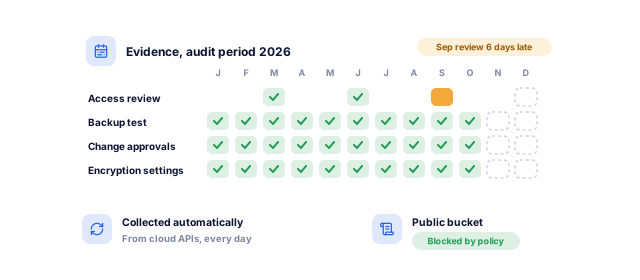
Automated evidence, scheduled access reviews and policy guardrails keep you ready between audits.
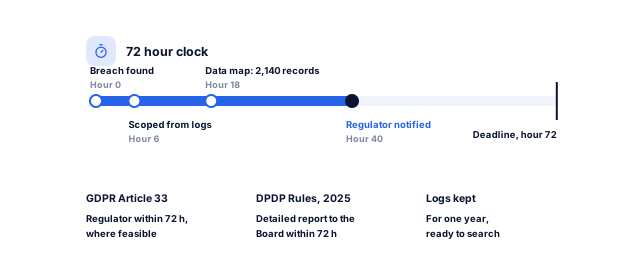
GDPR Article 33 asks for breach notice within 72 hours where feasible; India's DPDP Rules, 2025 require a detailed report within 72 hours and logs kept for a year. We prepare the plan in advance.
Give us read-only access to one account or subscription. We will send a written cloud security review with the top risks ranked by impact, and you can fix them with or without us.
Accounts, data and frameworks in scope, with read-only access agreed.
Everyone agrees what is in scopeScanners check the CIS Benchmarks; we review IAM, networks, keys and logs by hand and rank every finding.
An honest, ranked picture of riskCritical findings fixed first, in infrastructure as code, tested before production.
Critical gaps closedPolicies block public storage and unencrypted resources; every alert has a runbook.
Mistakes blocked before they shipControls mapped, policies written, evidence sampled the way an auditor would.
Ready for an independent auditorMonthly posture reports, quarterly access reviews and runbook tests.
Security that keeps up with changeThe controls are similar everywhere; the data and the rules change.
Your prospect wants SOC 2. We set up tenant isolation, staff SSO, reviewed changes and tested backups, or build them in with our SaaS application development team.
No cloud provider is HIPAA certified (AWS), so risk analysis and audit logs stay your job. We build them around systems such as a hospital management system and sign a BAA for US patient data.
Keep card data out of your cloud with hosted payment pages and tokenization, the cheapest PCI DSS control. Our ecommerce development team handles checkout changes.
GDPR and UK GDPR expect security matched to risk. Most DPDP obligations apply 18 months after the November 2025 notification; we close the gaps first.
We revoke credentials, isolate resources and preserve logs, then fix the root cause and add the missing guardrail, with our disaster recovery team if data needs restoring.
The same cloud controls usually serve several frameworks, so we map them together.
Book a strategy call| Framework | Who it applies to | What it asks of your cloud | What you show |
|---|---|---|---|
| SOC 2 | Service providers whose customers ask for assurance | Access, change management, logging, monitoring, incident response | A CPA firm's report: Type 1 at a point in time, Type 2 over several months |
| ISO/IEC 27001 | Any organization wanting certification | Risk assessment, Statement of Applicability, access, cryptography, logging, suppliers | Certification by an accredited body, then surveillance audits over three years |
| HIPAA | US covered entities and business associates | Risk analysis, access and audit controls, encryption, a BAA | No official certification; a documented risk analysis, policies and access records |
| PCI DSS | Anyone storing, processing or transmitting card data | A segmented card data environment, encryption, scans, logging | A self-assessment questionnaire or an assessor's report, by card volume |
| GDPR and UK GDPR | Anyone processing personal data of people in the EU or UK | Security matched to risk, processor agreements, lawful transfers | Processing records, impact assessments, breach notice within 72 hours where feasible |
| DPDP Act 2023 | Anyone processing digital personal data in India, or serving people there | Encryption or masking, access control, monitored logs, backups, processor contracts | Logs kept a year; a detailed breach report to the Board within 72 hours |
A summary, not legal advice. Sources: GDPR, the DPDP Rules, 2025, AWS HIPAA guidance and the AICPA.
The assessment sets the fix list and the weeks.
Book a strategy callBy week 3, you have a ranked fix list and a dated plan.
By the end, critical gaps are closed and blocked from coming back.
You enter the audit with evidence already flowing.
You approve each step before we change anything, and everything we set up stays in your accounts.
Yours to keep, always. Everything is set up in your name, and if you leave we remove our access and hand over the documentation.
For companies that must close security gaps and prove it.
Book a strategy callCertified engineers write the Terraform, change IAM policies and tune alerts; our developers fix application issues. With DevOps and CI/CD in-house, security checks run on every release.
We are not an audit firm, which keeps your auditor independent. We prepare controls and evidence, help you pick an audit firm, and build first what customers ask about.
An NDA before any access, and a DPA when you need one. Accounts, keys, logs and policies stay in your name; you can remove our roles at any time.
These numbers come from our SEO, marketing and software work, measured in each client’s own analytics. For your cloud, the first numbers come from the free review: what you spend, what is exposed, and how long a restore really takes.
See all case studies
MastersBuddyStudy abroad consulting
160+
keywords in Google's top 10
AkosMDHealthcare, Arizona
+57%
patient footfall
Eric OriginalsJewelry ecommerce
+1,900%
organic traffic
"From designing a high-converting website to managing our SEO, Google Ads, and Google Business Profile, improveFX delivered exceptional results across every channel."
 Maureen CappalloBroker and founder, Momentus Real Estate Group
"They revolutionized our online presence with a 60% increase in web traffic through strategic e-commerce SEO and content optimization."
 Eric NoahPresident, Eric Originals & Antiques Ltd.
"Visionstar Technologies' online presence transformed significantly with a 40% boost in customer engagement, all thanks to their exceptional website structuring and SEO tactics."
"Their strategic approach to our website and SEO resulted in a 60% increase in local inquiries, revolutionizing our automobile service business."
"Their SEO strategy helped us achieve top search rankings, while their Facebook Ads campaigns drove a steady flow of qualified prospects."
 Amita NaithaniCo-founder, Amita Naithani Resort Wear
Not seeing yours? Ask us directly and a specialist will reply personally.
Cloud security and compliance services include a security assessment, fixes to configuration and access, encryption, central logging, threat detection, policy guardrails, and control mapping with evidence for audits. With improveFX they also cover infrastructure-as-code changes, an incident runbook, written policies, a readiness review before your audit and optional monthly monitoring on AWS, Azure and Google Cloud, with an owner and a date for every fix.
Cloud security is the set of controls that protect your data and systems. Cloud compliance is proving those controls meet a specific framework or law, with evidence an auditor or regulator accepts. You can be secure but undocumented, or pass a narrow audit while real risks stay open, so good compliance work starts from real controls, then documents and evidences them.
Ongoing cloud management with improveFX runs from under $1,000 to $15,000+ a month, depending on your environment. One account and one framework sit at the low end; more accounts, environments, clouds, frameworks or support hours move it up. The assessment is quoted after a free security review. Your cloud bill from AWS, Microsoft or Google, and your auditor's fee, are separate from ours.
Both. Under the shared responsibility model, AWS, Azure and Google Cloud secure their data centers, hardware and core services, and you secure your configuration, identities, data and applications. Your share grows with the service type: on virtual machines you patch the operating system and set firewall rules, while on managed services the provider runs more, but permissions, encryption choices and data stay yours.
Readiness usually takes a few months, depending on how many controls already exist, and a SOC 2 Type 2 report then needs an observation period, often several months. Remediation drives the timeline more than paperwork: teams already using SSO, infrastructure as code and reviewed changes move faster. You get a dated plan after the assessment, and your auditor confirms the audit period.
No. Independent CPA firms issue SOC 2 reports, and accredited certification bodies issue ISO 27001 certificates. Keeping preparation and audit separate protects the auditor's independence, which is what your customers rely on. We prepare the controls, policies and evidence, help you shortlist audit firms, and fix anything raised during fieldwork, so your team is never left alone with the findings.
The rules of each market you serve: SOC 2, HIPAA and PCI DSS in the US; GDPR and UK GDPR, plus NIS2 and DORA where they apply, in Europe; PIPEDA in Canada; the Privacy Act, APRA CPS 234 and the Essential Eight in Australia; and the DPDP Act in India, with data kept in the regions you choose. Your counsel confirms what applies to you.
An engineer responds to critical incidents 24x7; other issues are handled in business hours. We contain first, preserve logs, fix the cause and send a written report of what happened and what changed. We sign an NDA before access is shared, and a DPA or BAA where you need one. Your accounts stay in your name, and you can remove our roles anytime.
Tell us what worries you about your cloud, or book a strategy call with our team.


 A specialist replies personally 4.9 from 566 client reviews